Cloudflare has launched a closed beta of a post-quantum version of GeoKey Manager, a service designed to restrict where customers’ private encryption keys can be unwrapped. The company says the new system is part of its Data Localization Suite and is intended to give organizations a technical control for keeping key use inside selected countries or regions.
The release is not generally available yet. Cloudflare said the closed beta begins now, while general availability is planned for the first quarter of 2027. Customers therefore need to treat the announcement as an early-access milestone rather than a finished deployment option across every Cloudflare product.
How the regional boundary works
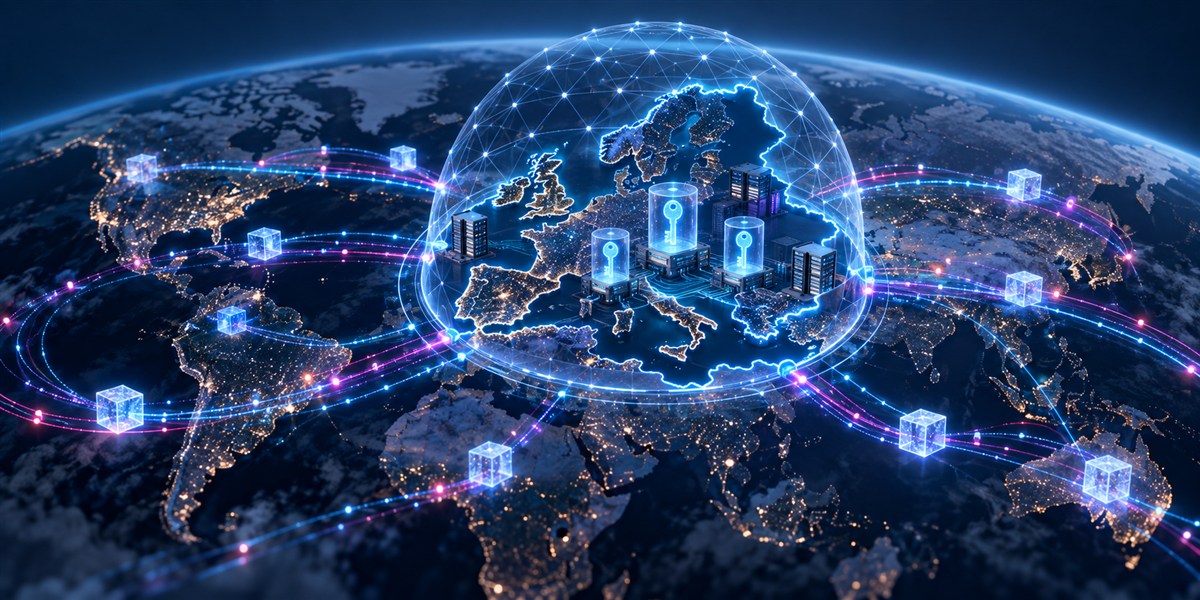
GeoKey Manager distributes wrapped customer keys across Cloudflare’s network, but the regional root keys needed to unwrap them follow a separate provisioning path. An edge server must prove its hardware identity and regional membership before it can receive the root keys authorized for that location. Cloudflare says those roots are loaded into the Linux kernel keyring rather than stored persistently on disk.
The design is meant to fail closed. If a server lacks the correct regional root key, or if its service context, region or key epoch does not match, the request is rejected instead of allowing the customer key to be used outside the selected geography. That approach can protect location rules, although it also makes correct provisioning essential for availability.
A hybrid post-quantum design
For the Cloudflare One path, the company says it combines ML-KEM-768 with the classical X25519 scheme inside Hybrid Public Key Encryption. HKDF-SHA-256 is used for key derivation and AES-256-GCM for authenticated encryption. Combining post-quantum and classical components is intended to preserve confidentiality as long as at least one remains secure.
Cloudflare is positioning the change against “harvest now, decrypt later” attacks, in which adversaries save encrypted data for possible decryption by future quantum computers. The company said the new GeoKey Manager will underpin an improved Regional Services offering for Cloudflare One. A separate integration is still being developed for the existing CDN key-location capability, so customers should verify which product paths are covered before relying on the beta.
For regulated buyers, the distinction between key location and complete data localization is important. GeoKey Manager controls where selected private keys can be unwrapped, but Cloudflare notes that Regional Services separately govern where traffic terminates, is inspected and is processed in plaintext. A compliance review should therefore assess the whole request path, not infer that regional key control alone keeps every data operation inside the same boundary.
Source: Cloudflare product and engineering announcement.
Featured image: AI-generated editorial illustration; not a photograph of a real event.