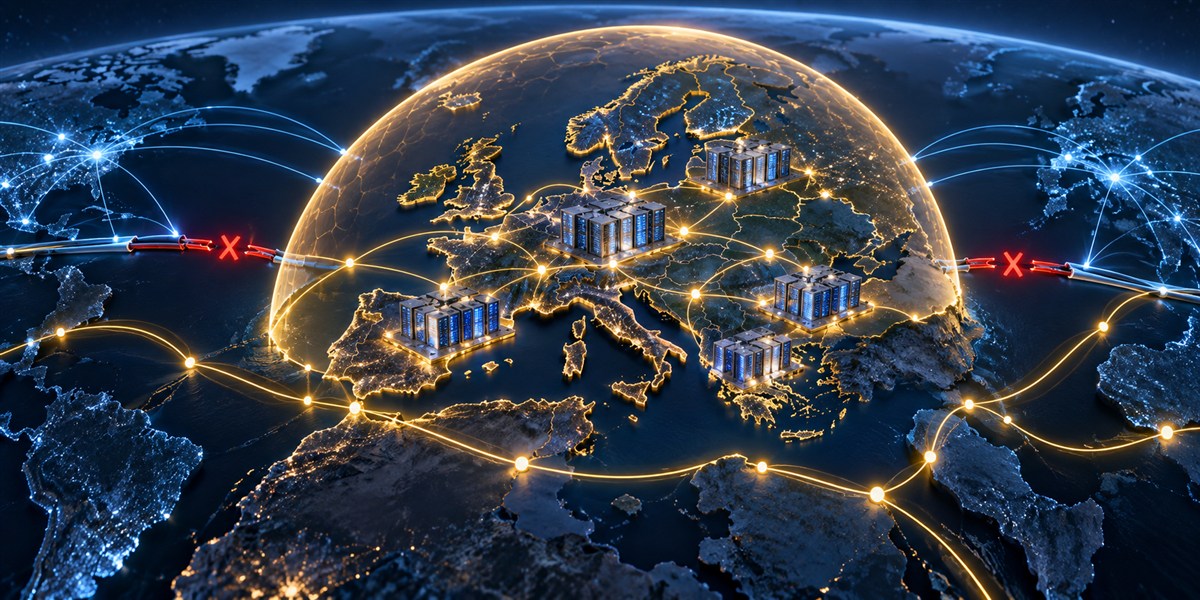
Amazon Web Services plans to disconnect its European Sovereign Cloud from the AWS Global Network backbone for several hours on October 24, 2026. The scheduled exercise is intended to demonstrate that the EU-based cloud can continue operating without dependence on infrastructure outside the European Union.
AWS announced the test in advance on September 28. Because the exercise is planned for later on October 24, its results should not be treated as complete until the company publishes evidence from the event. The current claim is about the design and expected behavior, not a verified outcome.
What AWS says will be disconnected
The AWS Global Network backbone is the company’s private network for moving authorized operational data between locations without using the public internet. During the exercise, AWS says the European Sovereign Cloud will operate without that backbone connection and the limited traffic involved will be rerouted securely over the public internet.
AWS says the change should not affect service availability inside the European Sovereign Cloud, other AWS Regions or customer private connectivity through Direct Connect. The company also described a separate system, controlled by the local EU team, for limited operational-data transfers. AWS says neither the backbone nor that transfer system is critical to operating the sovereign cloud.
Why the exercise matters
European public-sector and regulated customers increasingly ask cloud providers to show that operations, access and resilience can remain under regional control. AWS says the exercise is designed to produce technical and operational evidence aligned with the objectives of the European Commission’s Cloud Sovereignty Framework and criteria in Germany’s C3A cloud assessment framework.
A temporary disconnection can test routing, local staffing and operational procedures, but it is not the same as permanent isolation. Customers assessing sovereign-cloud claims should examine the duration of the test, which management functions remained local, what traffic used alternate paths and whether AWS publishes an independent or auditable account afterward.
The value of the test will depend on what AWS discloses after it ends. Useful evidence would include the exact start and end times, whether any service or control-plane functions degraded, how public-network routing was protected, which teams managed the event and whether customers observed measurable changes. Without that post-exercise record, the planned disconnection is evidence of intent and architecture, not proof that every sovereignty requirement has been met.
Bex News will treat any later operational results as a separate update rather than assuming the announced plan succeeded.
Source: AWS Security Blog announcement.
Featured image: AI-generated editorial illustration; not a photograph of the planned exercise.